Penetration Testing in Morocco: A Guide for Companies
Lire en français
How Moroccan companies can prepare, scope, and get value from a penetration test: authorization, evidence, retesting, and budgeting in MAD.
Table of contents
A penetration test (pentest) means attacking your systems, with written authorization, to find out which weaknesses are genuinely exploitable. For a Moroccan company, it is often the most direct way to know where to focus security effort — and to demonstrate it to a client, an auditor, or a regulator.
Why a pentest, not just a scanner
A vulnerability scanner lists possibilities: outdated versions, missing headers, questionable settings. A pentest answers a different question: can an attacker actually reach your data or disrupt your operations?
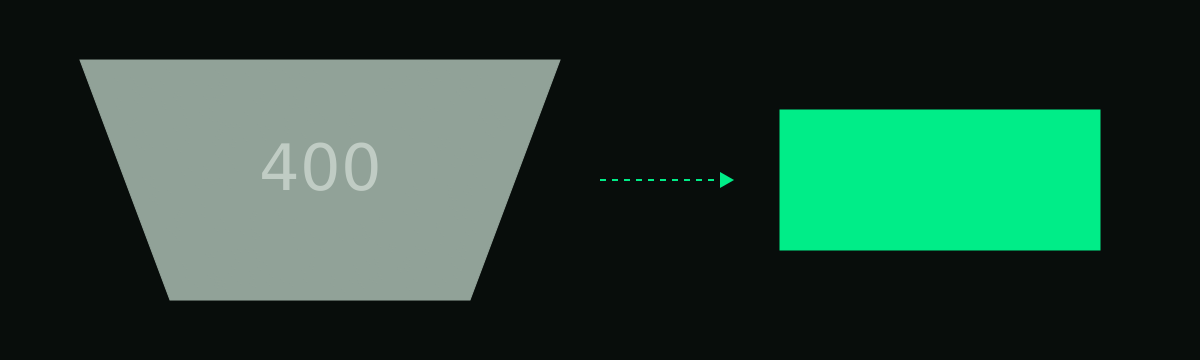
That difference drives prioritization. A team of three developers cannot fix 400 alerts. It can fix the five proven attack paths that lead to the customer database.
What to agree before testing starts
- Scope: domains, web applications, APIs, cloud environments, test accounts. Anything not listed is out of scope.
- Authorization: a document signed by someone empowered to approve it, listing targets, dates, and excluded techniques.
- Testing windows: production or staging, permitted hours, emergency contacts.
- Personal data: if customer data may be visible during testing, agree how it is handled, retained, and deleted.
Good first step. Start with your internet-facing assets and APIs. That is where most exploitable attack paths begin.
What you should receive at the end
A useful report is more than a list of CVEs. For every confirmed vulnerability, ask for:
- what was tested and how to reproduce the issue;
- the concrete impact, demonstrated on your scope;
- remediation guidance your developers can act on;
- a retest after the fix, proving the issue is closed.
Without a retest, you know there was a problem — not that it is gone.
One-off pentest or continuous validation?
An annual pentest is a snapshot. Your applications change every week. Continuous validation keeps the same principles — agreed scope, evidence, retesting — on a regular cadence that follows your releases.
| One-off pentest | Continuous validation | |
|---|---|---|
| Frequency | Once or twice a year | On an agreed cadence |
| Fix retesting | Often optional | Included |
| Tracks changes | No | Yes |
What budget to expect in Morocco
Cost mostly depends on scope: number of applications, API complexity, environments covered, and expected depth. Ask for a quote in Moroccan dirhams (MAD) that states what is included — especially retests and the evidence format.